In short: WordPress security is not solved by a single plugin. It is the sum of small steps applied regularly. Up-to-date software, strong passwords with two-factor authentication, a limited number of administrator accounts, correct file permissions, SSL and a backup you have actually tested will stop most attacks. You can work through the 10-step checklist below in order.
Because WordPress is so widely used, attacks are usually aimed not at one particular site but at every site carrying a known vulnerability. Automated scanners look for outdated plugin versions, weak passwords and exposed files. Even a small site is within the scope of these scans.
The entry points attackers use most often are:
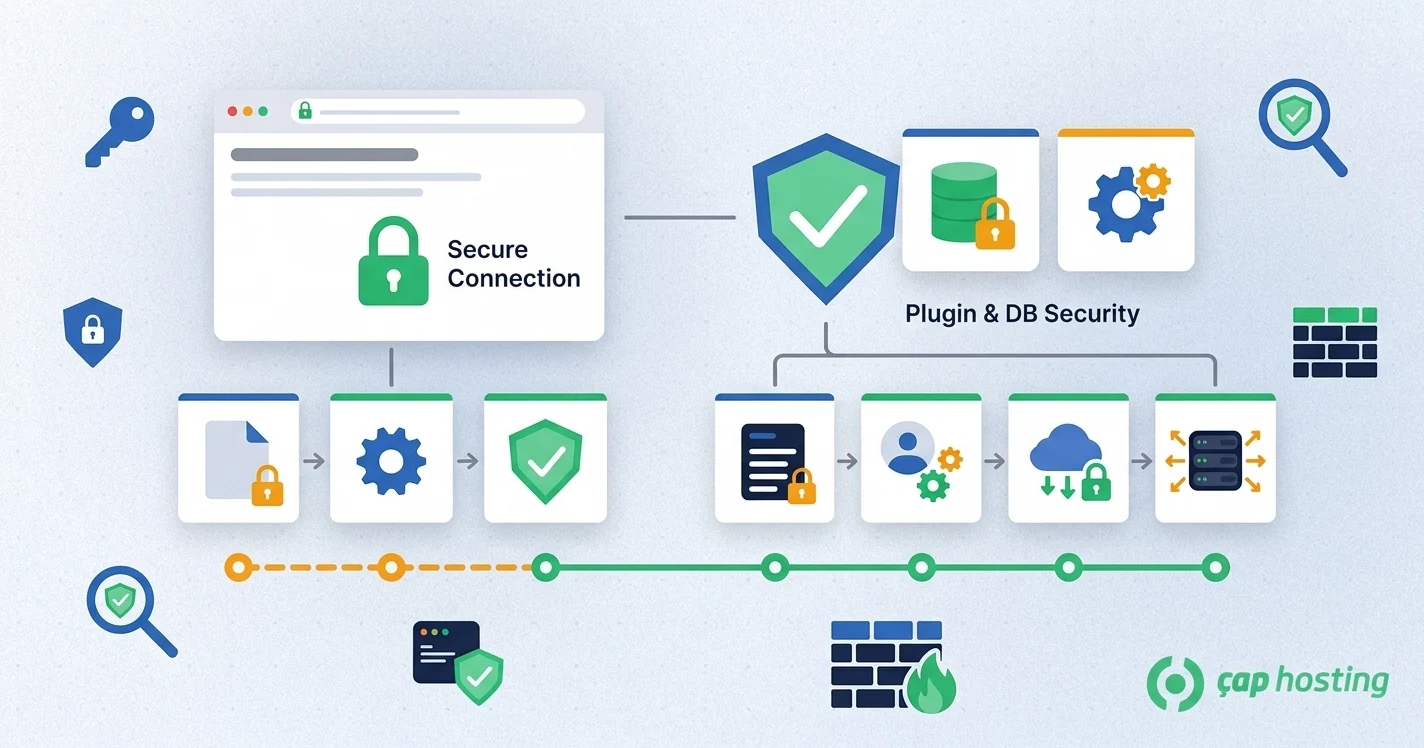
Security patches arrive through updates. WordPress installs minor releases automatically by default; for plugins and themes you can enable auto-updates one by one on the Plugins screen in the dashboard. Take a backup before major version upgrades.
The files of a deactivated plugin remain on the server and can still be exploited if they contain a vulnerability. Do not just deactivate unused plugins, delete them. Remove all themes except your active theme and one default theme.
Set a unique, long password for every account and store passwords in a password manager. Turn on two-factor authentication (2FA) for administrator and editor accounts; in WordPress this is added with a plugin. Even if a password is stolen, the second step blocks the login.
Give the administrator role only to people who really need it. The Editor or Author role is enough for people who enter content. Do not use "admin" as a username, and close the accounts of former employees and previous agencies.
By default WordPress does not limit failed login attempts. A plugin that restricts the number of attempts slows down password-guessing attacks. The same attacks can be carried out through XML-RPC, so disable that interface if you do not use it. The steps are covered in our guide on what XML-RPC is in WordPress.
Login details sent over an unencrypted connection can be read on the network. Serve your whole site over HTTPS and redirect HTTP requests to HTTPS. For the basics, see what an SSL certificate is; for the migration steps, see our HTTP to HTTPS migration guide.
As a general rule, directories run with 755 and files with 644 permissions. Use a stricter permission (for example 600) for wp-config.php, which contains your database password. Never set any directory to 777; if a plugin asks for it, the problem is file ownership, not permissions.
The theme and plugin editor in the dashboard lets anyone who takes over an account write code directly. You can disable the editor by adding this line to wp-config.php:
define( 'DISALLOW_FILE_EDIT', true );In addition, blocking PHP execution in the wp-content/uploads directory prevents an uploaded malicious file from running. On servers using Apache, add a .htaccess file with the following content to that directory:
<FilesMatch "\.php$">
  Require all denied
</FilesMatch>A backup is the only thing that brings your site back when every other measure has failed. Back up files and the database together, keep a copy off the server, and try a restore a few times a year. For details, see our article on website backup strategy.
PHP versions that have reached end of life no longer receive security patches. Run your site on a current PHP version that your theme and plugins are compatible with. You can change the version from your hosting control panel; this step also improves speed, as explained in our WordPress speed optimization article.
If you are looking for a comprehensive reference, the official WordPress hardening guide covers the technical details of these steps.
ÇAP Hosting hosting plans come with a free SSL certificate, PHP 8.x support and the CWP control panel, so you can manage the PHP version, file permissions and SSL from the panel. If you are setting up a new site, start with our WordPress installation guide, and if you get stuck on any step in this list, get in touch with us.
WordPress core receives regular security updates. Most problems do not come from core but from outdated plugins and themes, weak passwords and software from unknown sources. A WordPress site that is kept up to date and configured correctly can be used safely.
It is not mandatory, but it makes the job easier. Features such as login attempt limiting and two-factor authentication are not built into WordPress, so they are added with a plugin. A plugin complements update, password and backup discipline; it does not replace it.
Common signs are administrator accounts you do not recognise, content or links you did not add, visitors being redirected to other sites, titles in a foreign language in search results and an unexplained rise in resource usage. If you see these, change your passwords and restore a clean backup.
For most sites the benefit of auto-updates outweighs the risk, because vulnerabilities start being scanned for shortly after they are published. If you take regular backups, a faulty update can be rolled back. On critical e-commerce sites it is safer to try updates in a test environment first.
SSL encrypts the data between the visitor and the server and prevents login details from being read on the network. It does not stop plugin vulnerabilities or weak passwords. SSL is therefore necessary, but not sufficient on its own.
 Copyright © 2026 All Rights Reserved
 Turkey (Türkçe)
 Worldwide (English)