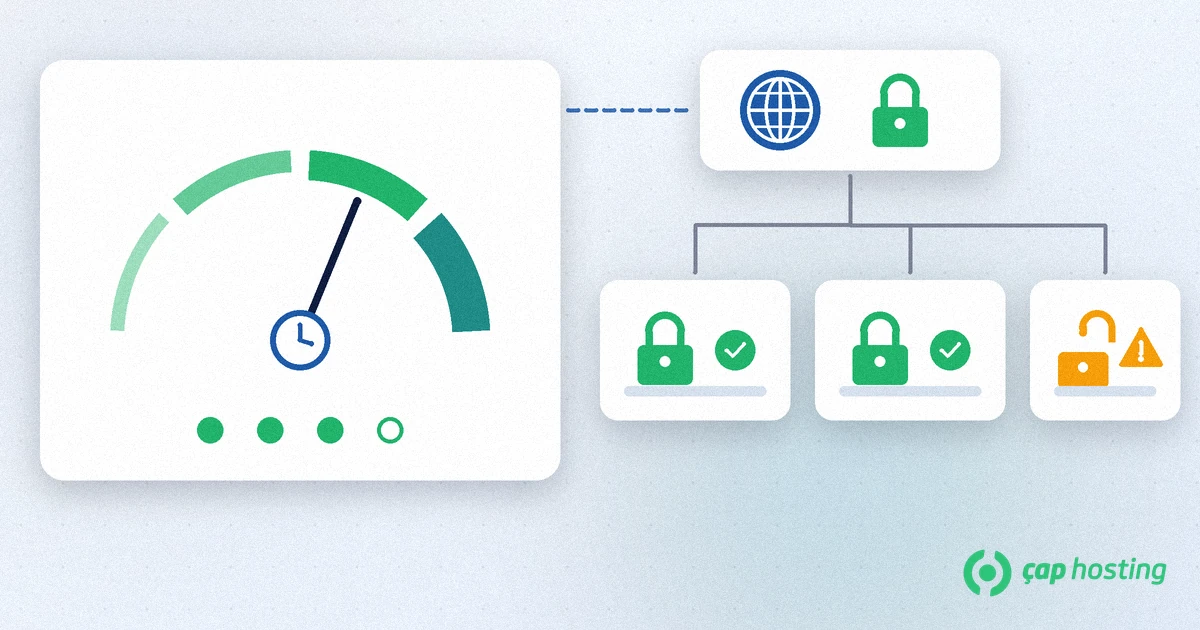
In short: What is HSTS? HSTS (HTTP Strict Transport Security) is a security header in which your server tells the browser "from now on, connect to this site over HTTPS only". The browser remembers that rule for the time you set, quietly turns http addresses into https and does not let visitors click through an invalid certificate warning. To use it safely, make sure every hostname you run works over HTTPS first, then enable the header with a short lifetime and raise it in stages.
You have moved your site to HTTPS and redirect every http address with a 301. That is a good start, but the very first request still travels unencrypted, and someone in the middle can tamper with that redirect. HSTS closes this gap. In this article we explain how HSTS works, what each setting in the header means, how to switch it on without locking yourself out and why you should not rush into the preload list.
HSTS is an HTTP response header called Strict-Transport-Security, defined in RFC 6797. When a browser receives this header over HTTPS, it adds the domain to its own HSTS list. According to the MDN documentation, from then on:
max-age in the header, and every new response starts that period again.One important detail: if the header is sent over plain HTTP, the browser ignores it. HSTS also applies to domain names only, never to IP addresses.
HSTS is aimed at an attacker sitting between the visitor and your server. Picture a visitor joining a fake Wi-Fi network in a café. Without HSTS, the browser's first http request can be read, and the attacker can block the redirect to https. hstspreload.org lists the cases HSTS helps with:
HSTS does not protect your application layer. Form attacks and malicious requests need separate measures such as a WAF (web application firewall).
| Setting | Meaning | Watch out for |
|---|---|---|
max-age | How many seconds the browser remembers the rule | A long value also means a long way back if you make a mistake |
includeSubDomains | Applies the rule to every subdomain as well | A subdomain without HTTPS becomes unreachable |
preload | Signals a request to join the preload list built into browsers | Should not be added by default; removal takes months |
Header always set Strict-Transport-Security "max-age=300; includeSubDomains"add_header Strict-Transport-Security "max-age=300; includeSubDomains" always;HSTS has one weak spot: on the very first visit, the browser does not know the rule yet. The preload list is a list of domains built into browsers to protect that first visit too. To apply, you need a valid certificate, an http to https redirect on the same host, HTTPS on every subdomain and a header on the base domain with a max-age of at least 1 year plus includeSubDomains and preload.
Even so, hstspreload.org recommends HSTS but does not recommend preloading. Many browsers already try to upgrade http navigations to https, so the extra benefit of preloading is limited, while getting removed from the list can take months. If you are not sure that every subdomain will run on HTTPS for the long term, leave preload out.
curl -sI https://yourdomain.com | grep -i strict-transport-security shows the header and its value.strict-transport-security line in the response headers.chrome://net-internals/#hsts you can query your domain and see the rule the browser has stored.max-age=0 over HTTPS.HSTS is the final security step for a site that has moved to HTTPS: it tells browsers to reach the site over encrypted connections only and stops visitors from clicking through certificate errors. Finish HTTPS and your redirects first, check your subdomains, enable the header with a short lifetime and raise it in stages, and only consider preload as a long-term decision. If you are not sure where to add the header for your site at ÇAP Hosting, our support team can work through it with you.
HSTS is not a ranking setting in itself. It does make sure visitors and search engines consistently reach the HTTPS version of your site. You still need 301 redirects for the move to HTTPS itself.
Yes. When you send the header with max-age=0 over HTTPS, browsers delete the rule. This only takes effect in browsers that visit the site again, and removal from the preload list can take months.
Start with 300 seconds, then move through the 1 week and 1 month stages. If nothing breaks, use a long value such as 1 year. A preload application needs at least 31536000 seconds.
No. HSTS cannot be used without a valid SSL certificate and a working HTTPS setup. It only makes sure the browser always uses that secure connection.
 Copyright © 2026 All Rights Reserved
 Turkey (Türkçe)
 Worldwide (English)