In short: A mixed content error happens when a page loaded over HTTPS still tries to load some of its resources, such as images, scripts, stylesheets or fonts, from an unencrypted http:// address. The browser may then remove the padlock from the address bar, show a "not secure" warning or refuse to load the resource at all, which breaks part of the page. The fix is to find every http:// reference on the page and change it to https://: first spot the failing resources in the browser console, then correct the old addresses in the database and in theme and plugin files.
"Mixed content" means that secure (HTTPS) and insecure (HTTP) resources appear together on the same page. Even if the page itself is encrypted with an SSL certificate, a single embedded http:// resource lets an attacker read or change that resource on its way to the visitor. That is why browsers take mixed content seriously (MDN: Mixed content).
The error usually appears after a site moves from HTTP to HTTPS. The certificate is installed and the site opens with https://, but old http:// addresses saved over the years in posts, theme settings and plugin options stay where they were. For every step of the move, see our HTTP to HTTPS migration guide; this article focuses on the mixed content that is left over afterwards. If you want a quick summary of what a certificate does, read what is an SSL certificate.
Browsers split mixed content into two groups:
As a result, a mixed content error can show up with two different symptoms: the padlock in the address bar disappears or turns into a warning, or menus, sliders, forms or the design stop working. In the second case the visitor may never see a security warning, but the site looks broken.
Write the addresses you find in a list and group them by source: content in the database, theme files, plugin settings and external resources. Each group is fixed in a different way.
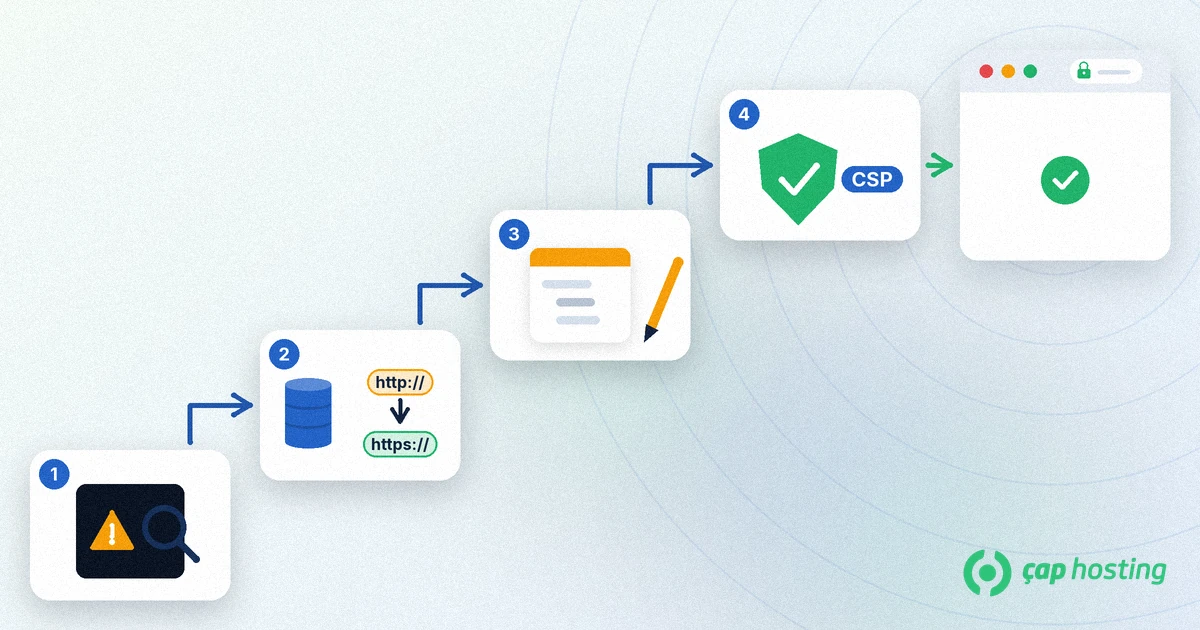
search-replace command is built for this and changes WordPress serialized data without breaking it. Run it with --dry-run first to see how many records will change (WP-CLI search-replace):
wp search-replace 'http://example.com' 'https://example.com' --dry-runIf the result is what you expect, run the same command without
--dry-run. Running a plain text replace query directly in the database is not recommended, because it can break serialized data.upgrade-insecure-requests directive of the Content-Security-Policy header tells the browser to make the page's http:// requests over https:// instead. On Apache servers you can add this line to the .htaccess file:
Header always set Content-Security-Policy "upgrade-insecure-requests"The directive catches what is left, but it does not replace the real fix: if the resource is not served over HTTPS the request fails and the browser does not fall back to HTTP (MDN: upgrade-insecure-requests). It does not replace HSTS either; see what is HSTS for the difference.
If the error still seems to be there after your fixes, the most common reason is caching. If you use a page cache plugin, a CSS and JavaScript optimisation plugin or a CDN, clear their caches, then empty your own browser cache as well. The steps for each browser are in our clear browser cache article. Then open the console again and recheck the same pages: no "Mixed Content" warning should remain and the padlock in the address bar should look normal.
Once the mixed content is fixed, our WordPress security checklist is a good next step for reviewing the overall security of your site.
No. The certificate can be perfectly valid; the problem is that the page still loads some resources from http:// addresses. Replacing the certificate does not fix this error.
Some plugins rewrite addresses in the page output on the fly, but that is not a permanent fix. Correcting the addresses in the database and theme files is the cleaner solution.
Browsers retry images, audio and video over HTTPS; if the resource is not served over HTTPS it fails to load. Scripts, stylesheets and iframes coming from http:// are blocked outright.
Not on its own. The directive upgrades the remaining requests to HTTPS, but if a resource is not served over HTTPS the request fails. The real fix is correcting the addresses at their source.
 Copyright © 2026 All Rights Reserved

 Turkey (Türkçe)
 Worldwide (English)
